
How to Protect AI-Generated Marketing Content Beyond DRM

AI has made creating marketing content dramatically easier.
It has also made copying, modifying, republishing, and impersonating branded content easier.
A marketing team can now create:
- product videos;
- AI-generated ads;
- webinars;
- online courses;
- branded images;
- social videos;
- premium reports;
- virtual presenters;
- personalized creative;
at a scale that would have been difficult a few years ago.
That creates a new marketing problem:
How do you protect all of it once it leaves your content management system?
Digital Rights Management, or DRM, can control access to protected content.
But DRM is only one layer.
Once legitimate content is displayed, streamed, shared, transformed, or distributed across third-party platforms, marketers may also need:
- watermarking;
- content fingerprinting;
- provenance metadata;
- copyright monitoring;
- behavioral analytics;
- brand monitoring;
- platform copyright tools;
- takedown processes.
This matters even more as AI becomes part of everyday marketing production.
Google now adds invisible SynthID watermarks and C2PA metadata to images and videos generated using Google Ads AI tools.
Adobe automatically adds Content Credentials to fully AI-generated Firefly assets.
And platforms such as YouTube have built increasingly sophisticated systems for finding duplicate copyrighted content.
The future of digital content protection is therefore not:
DRM or AI.
It is:
access control + attribution + provenance + detection + enforcement.
Chapters
Key Takeaways
- DRM can be circumvented through four documented categories, but each requires technical expertise, specific hardware, or privileged access that casual pirates do not have.
- The four bypass methods are: screen recording on Widevine L3 software DRM, HDCP downgrade and HDMI stripper attacks, Widevine L3 content key extraction, and insider sharing or account compromise.
- Each method maps to a specific countermeasure: forensic watermarking, hardware HDCP enforcement, Widevine L1 TEE-based key isolation, and behavioral session analytics with concurrency controls.
- The security research community has documented these vulnerabilities since the MovieStealer paper that was published by the University of California, Santa Barbara, which was included in the 22nd USENIX Security Symposium in 2013). Widevine L3 key extraction was publicly demonstrated by David Buchanan in 2019 and further investigated by Neodyme in 2021.
- MUSO’s annual piracy intelligence reports confirm that the overwhelming volume of piracy is casual and access-driven, which is precisely the category DRM addresses most effectively.
- The complete piracy defense architecture is: DRM + forensic watermarking + behavioral analytics. No single layer is sufficient. Together, they create a stack where what bypasses one layer gets caught by the next.
Digital Content Protection Statistics Marketers Should Know
More than 4 million YouTube channels can use Copyright Match
YouTube reports that more than 4 million channels have access to its Copyright Match Tool.
The system automatically identifies copies or potential copies of videos uploaded to other channels.
YouTube processed more than 2 billion Content ID claims
YouTube’s Content ID system generated more than 2 billion copyright claims during its latest reporting period.
Content ID is primarily used by rights holders with large or complex catalogs, including media companies, music labels, and studios.
More than 90% of Content ID claims are monetized rather than blocked
Content protection does not always mean removing copied material.
YouTube reports that rights holders chose to monetize more than 90% of Content ID claims.
That is an important marketing lesson.
Unauthorized distribution can sometimes become:
- revenue;
- attribution;
- additional reach;
rather than automatically becoming a takedown.
Google has watermarked more than 180 billion AI images and videos
Google reports that SynthID has been used to watermark more than 180 billion images and videos.
SynthID embeds an imperceptible signal into AI-generated media to help identify its origin.
Google Ads applies invisible AI provenance signals
Google says assets generated using its AI advertising tools can include:
- invisible SynthID watermarks;
- C2PA machine-readable metadata.
This makes content provenance directly relevant to marketers, not just publishers or photographers.
Why DRM Alone Is Not Enough for Marketing Content
DRM is designed primarily to control authorized access to digital content.
That is useful for:
- paid video;
- online courses;
- subscription media;
- premium presentations;
- members-only resources.
But marketers distribute content across environments they do not completely control.
A campaign might travel through:
Website → YouTube → LinkedIn → Partner → Influencer → Customer → Social repost
At that point, access control alone cannot solve every problem.
The content protection question changes from:
“Can this person open the file?”
to:
“Can we identify where this content came from, detect unauthorized copies, and respond appropriately?”
That requires several layers.
The StoryLab.ai AI Marketing Content Protection Stack
| Protection Layer | Main Purpose | Marketing Example |
|---|---|---|
| Access Control / DRM | Control who can access protected content | Paid course or premium video library |
| Visible Watermark | Deter obvious copying and communicate ownership | Agency preview or unreleased campaign creative |
| Forensic Watermark | Trace leaked copies back to a session or recipient | Pre-release video sent to partners |
| AI Watermark | Identify AI-generated content | SynthID embedded in AI-generated advertising assets |
| Content Credentials | Record how content was created or edited | Adobe Firefly marketing image with provenance metadata |
| Content Fingerprinting | Detect matching copies on platforms | YouTube Copyright Match or Content ID |
| Brand Monitoring | Find unauthorized or misleading reuse | Fake ads using company creative |
| Behavioral Analytics | Identify suspicious usage patterns | One premium account being accessed abnormally |
| Copyright Enforcement | Remove or monetize unauthorized copies | Copyright removal request |
What DRM Actually Does (And What It Was Always Designed to Do)

Before examining where DRM falls short, it is worth being precise about what it was built to accomplish. DRM has a clear and specific scope. Understanding that scope makes the bypass categories easier to evaluate objectively.
DRM (Digital Rights Management) is a system that encrypts content and requires a valid license from a trusted key server before a device can decrypt and play it. Without that license, the video file is unreadable ciphertext.
With it, the device receives the content key needed to decrypt and render the stream. No valid license means no playback, regardless of whether the user has the file.
The license is not issued arbitrarily. It is tied to the user’s authenticated session, the device, and the platform’s entitlement rules. A user who is not subscribed, not authenticated, or operating on a device that fails the platform’s security checks will not receive a license. That is DRM doing its job.
Is DRM fully secure? Not unconditionally. But it was never designed to be an unbreakable vault. It was designed to make casual piracy economically irrational, meaning that the effort required to bypass it far exceeds the cost of simply paying for legitimate access. On that specific objective, it succeeds. The question is what it does not cover.
How DRM Licenses Control Playback
At the center of how video DRM works is the Content Decryption Module, or CDM. A CDM is the software component embedded in browsers and certified devices that handles all decryption operations within a protected execution environment.
When a user presses play, the CDM sends a license request to the platform’s key server. The server verifies the session, confirms entitlements, and issues a license containing the content key. Only then does the CDM decrypt the stream and allow it to render.
The encryption standard used throughout this process is typically AES (Advanced Encryption Standard), which is computationally infeasible to break by brute force with current technology.
The security of the system, therefore, does not rest on cracking AES. It rests on controlling who can obtain a valid license and ensuring the content key is never exposed in a form an attacker can read.
That second condition, keeping the content key protected, is where the architecture differs significantly between DRM security levels.
Why Widevine Security Levels Change Everything
Widevine is Google’s DRM system. It is the most widely deployed DRM in streaming today, used by platforms operating on Android, Chrome, and most non-Apple devices.
Apple uses FairPlay, and Microsoft devices use PlayReady. Most enterprise streaming deployments implement all three in a multi-DRM architecture to cover every major device category.
Within Widevine, there are two security levels that matter for this discussion.
Widevine L1 means decryption happens inside a Trusted Execution Environment (TEE), a hardware-isolated processing environment built into the device’s chipset. The TEE is physically separated from the main OS and application layer.
The content key is generated, used, and discarded entirely within the TEE. It never enters accessible memory. The main operating system cannot read it, and no software running on the device can observe it.
Widevine L3 means decryption happens in software, typically inside the browser or application process. There is no TEE involvement.
The content key must exist in software memory at some point during playback. L3 is what most PC browsers use, and it is why major platforms cap L3 streams at standard definition quality.
That quality ceiling is not a content limitation. It is a deliberate security decision based on the key exposure risk that L3 creates.
The 4 Known Ways DRM Gets Defeated
The security research community has been studying DRM bypass categories since at least 2013.
The MovieStealer paper, published by researchers at UC Santa Barbara at USENIX Security 2013, examined how software-layer DRM systems could be defeated at the decode stage, establishing early academic documentation of the key exposure problem that later research would revisit.
That early work set the template for what followed: researchers identifying specific architectural gaps in the DRM stack, publishing findings with enough precision to be credible but without providing operational toolkits. Understanding why DRM fails in specific cases is how the industry improves its defenses.
What follows are the four documented bypass categories, each mapped to the specific control that addresses it.
Method 1: Screen Recording on Widevine L3 and Software-Only DRM
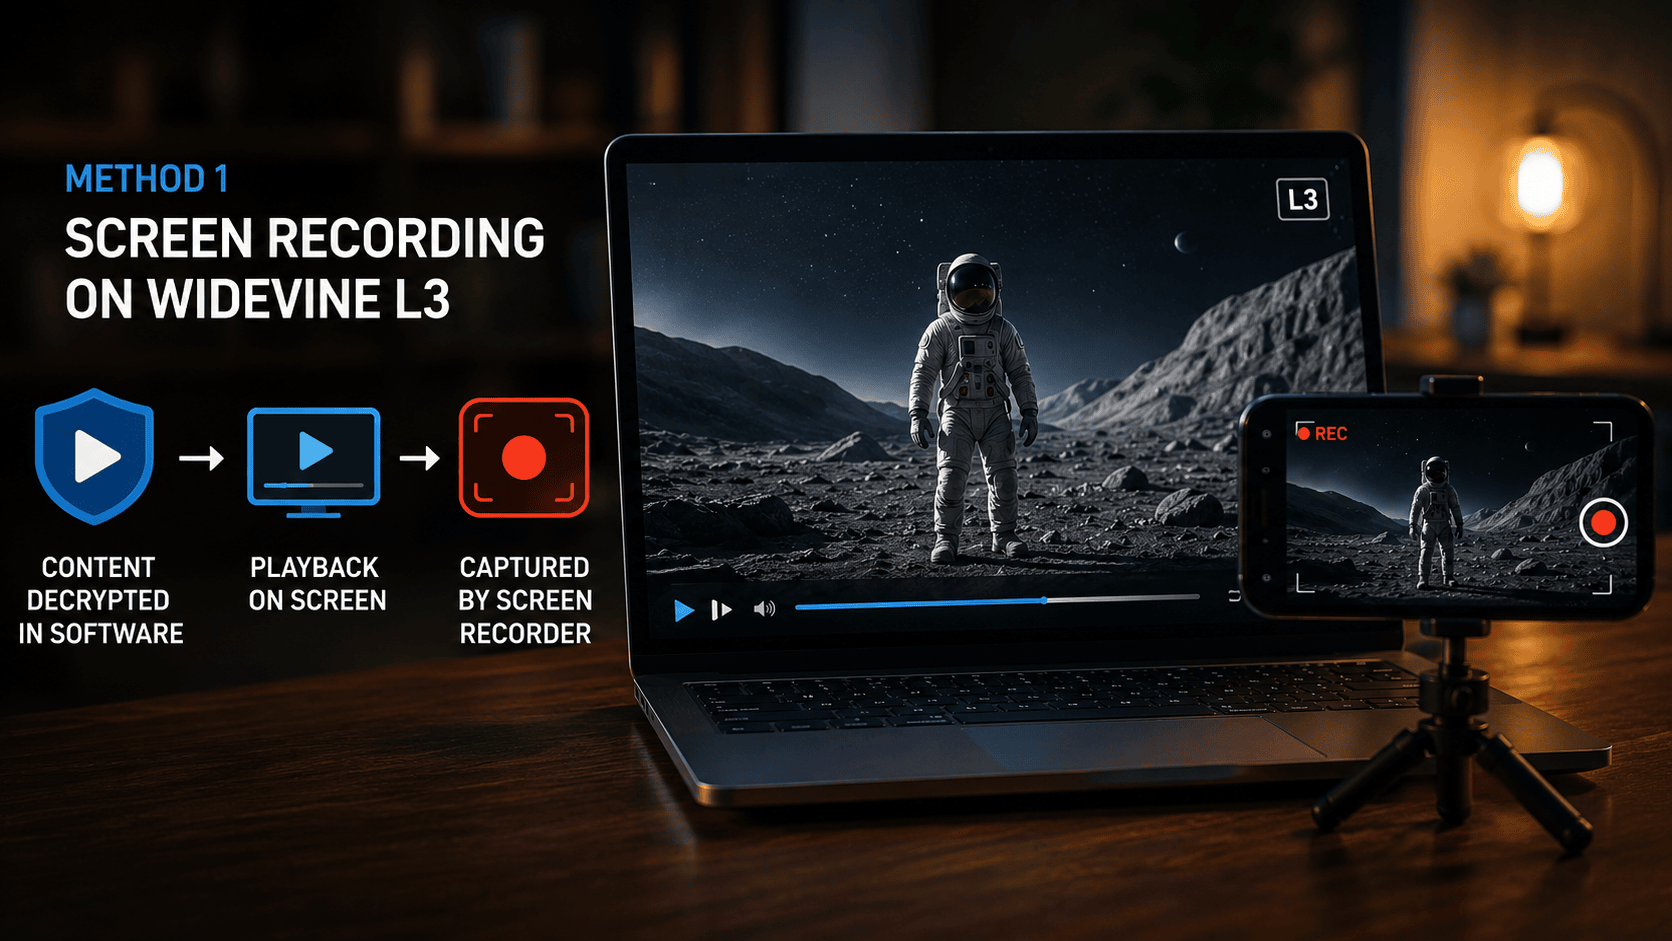
Widevine L3 is the software-only DRM implementation that runs in browser environments on most desktop and laptop devices.
Because decryption happens in software rather than inside a hardware-isolated TEE, the decrypted video frames have to pass through the device’s graphics pipeline before they reach the screen. That pathway through the render pipeline is the specific attack surface this category exploits.
Understanding this method requires separating what it is from what it is not. It is not a cryptographic attack. AES encryption is not being broken. The attacker is not intercepting the content key or cracking the license server.
The capture happens at the output stage, after the DRM system has done its job, at the point where decrypted frames are written to the display buffer.
Why Software-only Environments Create a Recording Window
In a software DRM path, decrypted video frames must be rendered by the GPU and delivered to the display.
A screen capture tool operating with sufficient system-level access can intercept those frames at the render output stage, before they reach the physical screen. The result is a recording that looks identical to the content being played, with no encryption to defeat.
This is why major streaming platforms restrict Widevine L3 to standard definition. Even if a recording is made at the software render stage, the quality ceiling limits its commercial value.
A 480p recording of a film that streams at 4K on Widevine L1-certified hardware does not compete with the original. The ceiling is a deliberate deterrent, not a technical limitation of the content.
Think of it like a bank securing a vault but allowing cashiers to count money in an open room. The vault itself is never compromised. What gets photographed is the output of a process that had to happen in the open.
The implication for content protection is direct: on any device that relies on L3, the decryption chain has an observable output stage.
How Forensic Watermarking Closes the Gap
The control that addresses screen recording at the software render stage is forensic watermarking.
Forensic watermarking embeds a unique, invisible identifier into each individual video stream at the session level. This identifier is tied to the specific viewer, session ID, or delivery token, not to the content file itself.
Every viewer watching the same video receives a perceptually identical stream with a different embedded marker.
This is fundamentally different from a visible watermark, which is the translucent overlay bearing a username or timestamp that users sometimes see in corporate training videos. A visible watermark deters casual sharing but can be cropped out by anyone with basic video editing software.
A forensic watermark is embedded in the video signal itself, survives re-encoding, compression, and format conversion, and is entirely invisible to the viewer.
The practical implication is significant. Forensic watermarking does not prevent screen recording. It transforms an undetectable screen recording event into a traceable one. If the recording is redistributed anywhere, the embedded identifier travels with it.
When the leaked copy is found, the watermark identifies the exact session that produced it. Enforcement action becomes possible where it was previously impossible.
That shift, from prevention to traceability, is the architectural contribution watermarking makes that DRM alone cannot.
Method 2: HDCP Downgrade and HDMI Stripper Attacks
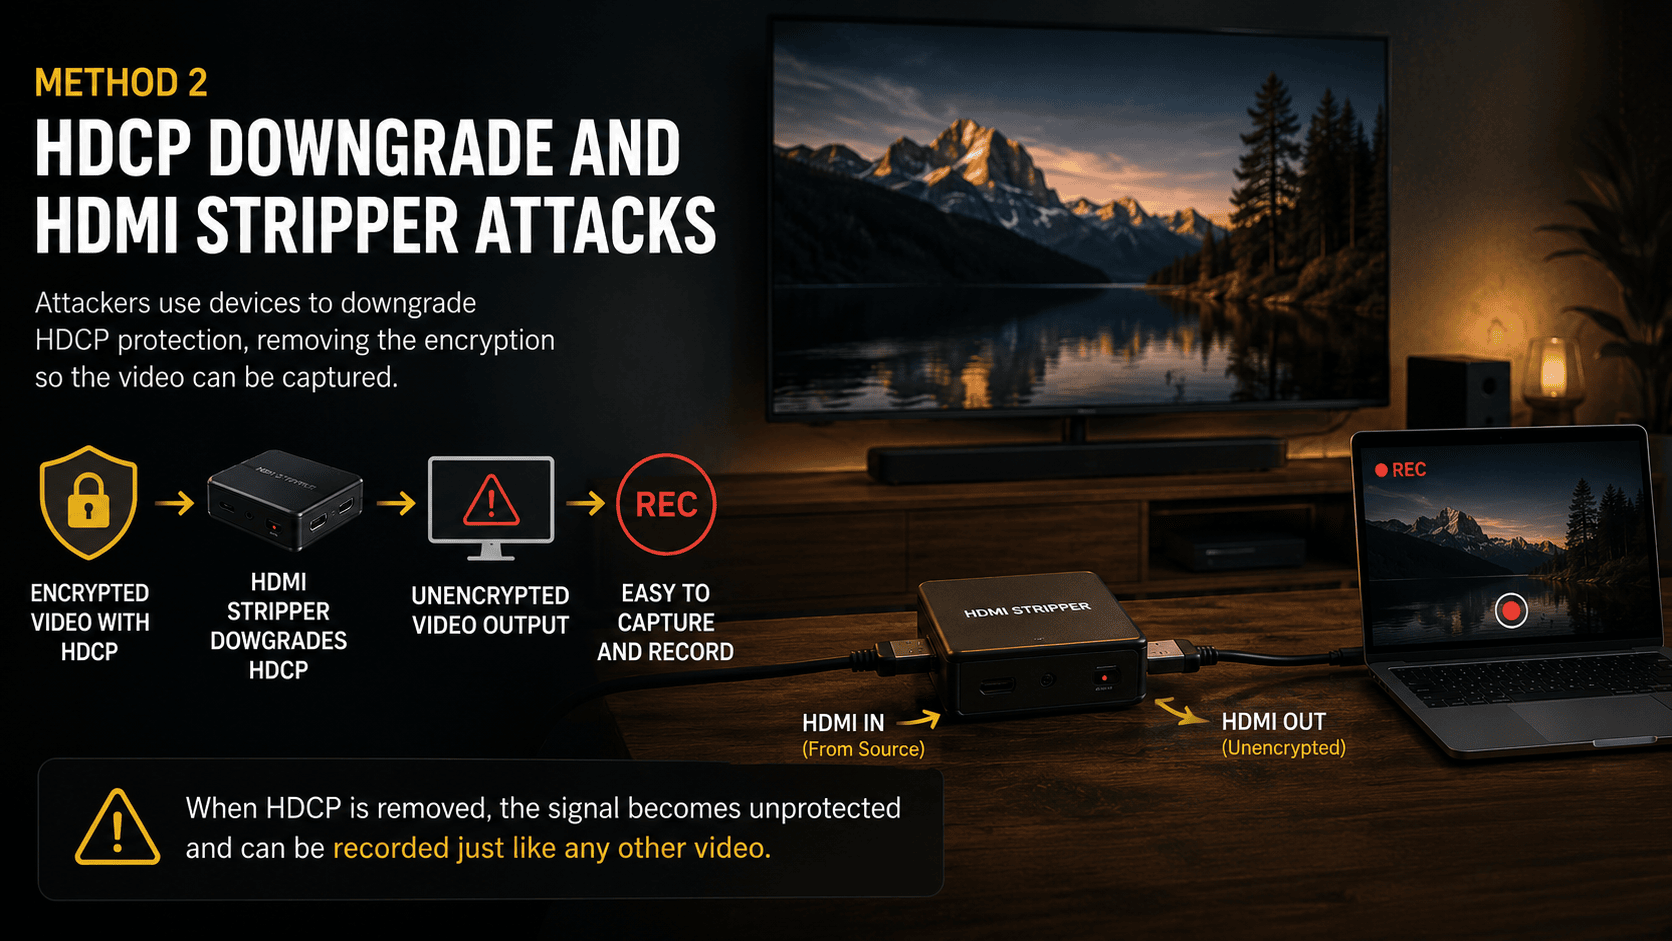
Content protection in a streaming setup does not stop at the software layer. The moment video travels from a streaming device to a television over HDMI, it passes through a separate hardware protection standard that operates entirely independently of DRM.
That standard is HDCP (High-bandwidth Digital Content Protection), and its failure modes are a different attack surface entirely.
This is a hardware-layer attack category, not a software exploit. The DRM system running on the streaming device is not compromised. What is attacked is the output path after the device has decrypted and prepared the video for display.
What HDCP Does and Where it Breaks Down
HDCP is a standard developed by Intel that encrypts the HDMI signal between a source device (such as a streaming box or smart TV app) and a display, ensuring that content in transit over the cable is not in cleartext.
Without HDCP, the signal traveling through the HDMI cable could, in principle, be intercepted and captured directly.
HDCP strippers are hardware devices designed to sit in the signal path between the streaming source and the display. They exploit implementation weaknesses in certain HDCP handshake versions to force a downgrade in the protocol, causing the source device to output video in a less protected state.
Once the stripper achieves the downgrade, it can capture the video signal from the cable before it reaches the television.
This attack requires physical access to the playback setup. An attacker needs to be physically present at the device, which inherently limits the scale at which it can be deployed.
Coordinated large-scale piracy through HDCP stripping is logistically impractical. What it does enable is targeted extraction of high-value content in controlled environments, such as a preview screening or a corporate content review session.
The Hardware Enforcement Control That Addresses This
The structural fix for HDCP downgrade attacks operates at two levels:
First, Widevine L1 enforcement at the CDM level requires that the device verify HDCP compliance on the connected display before outputting any protected content.
A device certified for L1 playback checks that the display and cable support the required HDCP version before the video is released to the HDMI output at all.
Second, platform policies that require HDCP compliance as a prerequisite for playback on certain device categories prevent the content from reaching the output path in high-quality form unless the full protection chain is intact.
If the display, the cable, or the connection cannot confirm HDCP compliance, the platform either degrades the stream quality to a level with lower commercial value or blocks playback entirely.
The combination of L1 enforcement and HDCP compliance gating means that a stripper placed in the signal path encounters either no signal or a degraded one.
The attack surface is not eliminated, but it is narrowed to a point where scale is essentially impossible for a motivated pirate without extraordinary physical access.
Method 3: Widevine L3 Content Key Extraction
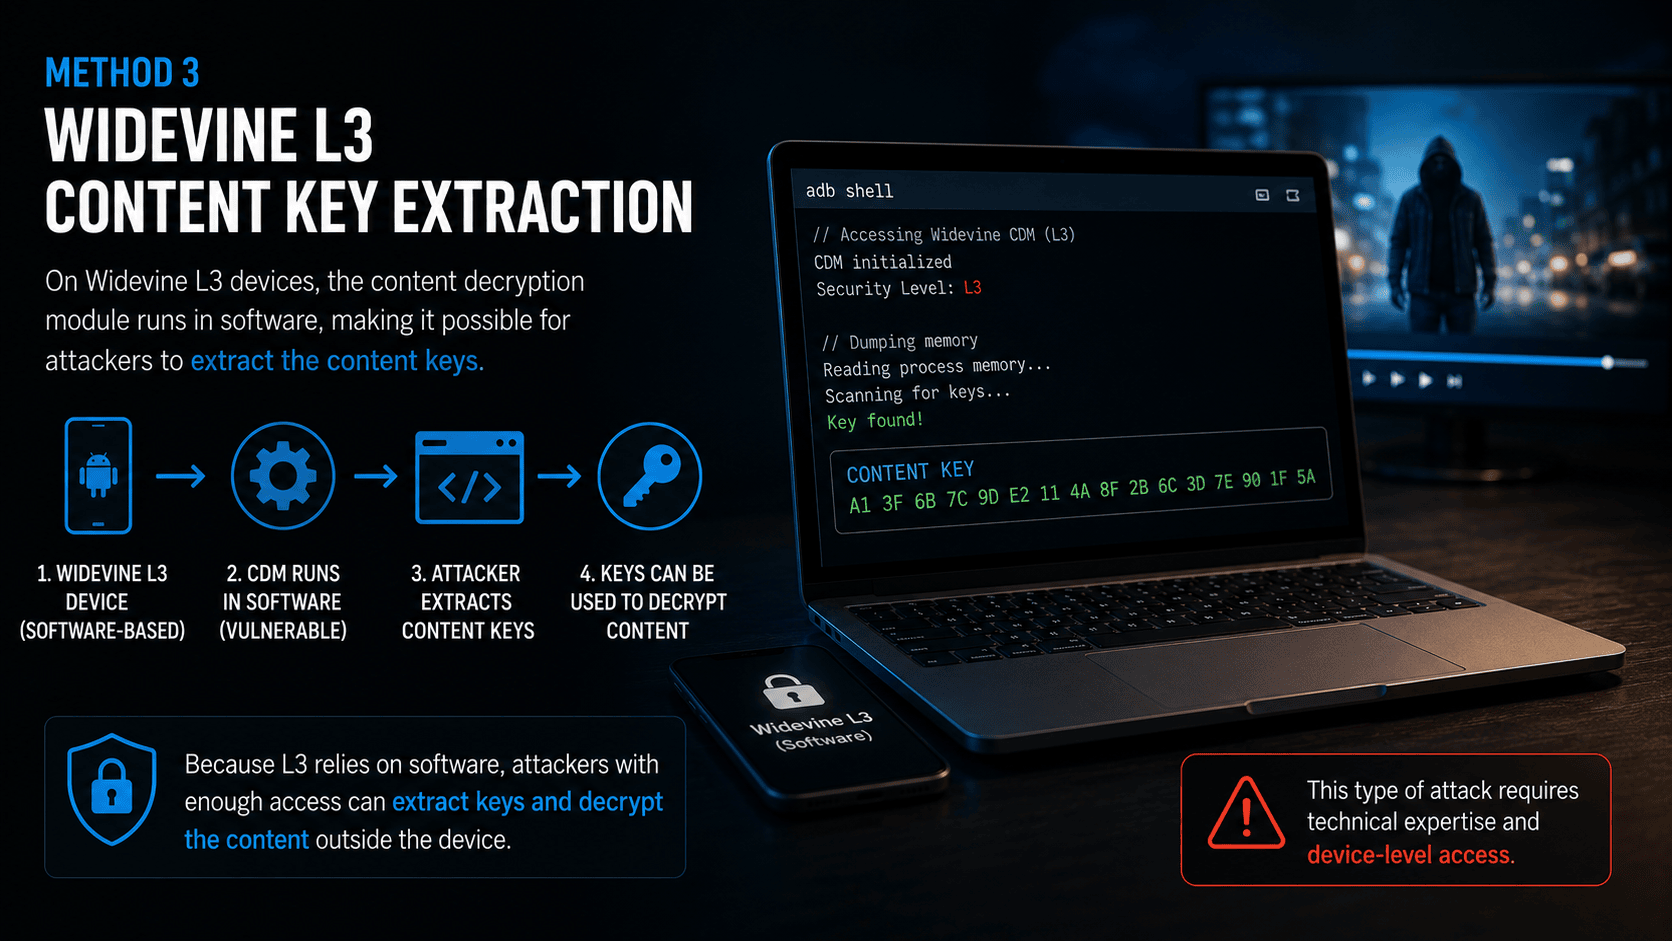
The most technically demanding bypass category on this list targets a structural property of software-based DRM that has been examined closely by security researchers.
Because Widevine L3 runs entirely in software, the content decryption key must at some point exist in memory accessible to the application layer. That specific property is what makes L3 vulnerable to key extraction.
This is not a theoretical concern. Documented research has confirmed the practical reality of this attack surface, and the findings have shaped how serious platforms think about DRM level enforcement.
What the Research Has Documented
In 2019, security researcher David Buchanan published a documented demonstration of Widevine L3 key extraction from a software CDM.
The research showed that under specific conditions, the content key used by the L3 implementation could be retrieved from memory during an active playback session. The findings were responsibly disclosed and are referenced in DRM security literature as a foundational demonstration of the software key exposure problem.
In 2021, security research firm Neodyme published further work examining the same Widevine L3 attack surface, adding depth to the body of documented findings on software CDM vulnerabilities.
Earlier academic groundwork came from the MovieStealer paper, published by researchers at UC Santa Barbara at USENIX Security 2013. That paper examined how software-layer DRM implementations could be defeated at the decode stage, establishing the conceptual framework that later practical research would build on.
To be clear about the category: these demonstrations show that a content key can be extracted from a software DRM implementation by a technically equipped researcher. They do not mean DRM keys are trivially accessible to ordinary users.
The skill level required is significant. The findings are relevant here because they confirm a documented architectural gap, not because they represent a widespread operational threat.
To be precise about what the research established: Buchanan’s 2019 demonstration confirmed that L3 content keys are accessible in process memory during active playback sessions. Neodyme’s 2021 work demonstrated that this surface persisted across subsequent Widevine CDM versions.
Neither publication provided a deployable tool, both disclosed responsibly to Google. The body of documented findings makes one architectural conclusion unavoidable: software-layer DRM cannot protect high-value content the way hardware-isolated TEE-based DRM can.
Why Widevine L1 Requirement is the Structural Fix
The reason Widevine L1 exists is precisely to eliminate the attack surface that L3 key extraction exploits.
In an L1 implementation, the content key is generated, stored, and used entirely within the Trusted Execution Environment (TEE), a hardware-isolated processor partition that the main operating system and application layer cannot access, even with elevated system privileges.
The key never enters RAM in a form that software can observe. There is no memory address, no process context, no accessible space where the key can be read by an attacker operating at the application layer.
This is why HD and HDR playback is unavailable on most PC browsers for premium platforms. It is not that the platform lacks HD content or that the browser lacks the processing power to render it.
It is that most PC browsers do not have access to a certified TEE. Delivering HD content through a Widevine L3 path would expose that content to the key extraction attack surface that David Buchanan and Neodyme documented. Requiring L1 for high-value content is the structural response to that documented gap.
The citable claim here is direct: Widevine L1 eliminates the software key extraction attack surface by ensuring that content keys never exist in memory accessible to the application layer.
Method 4: Insider Sharing and Account Compromise
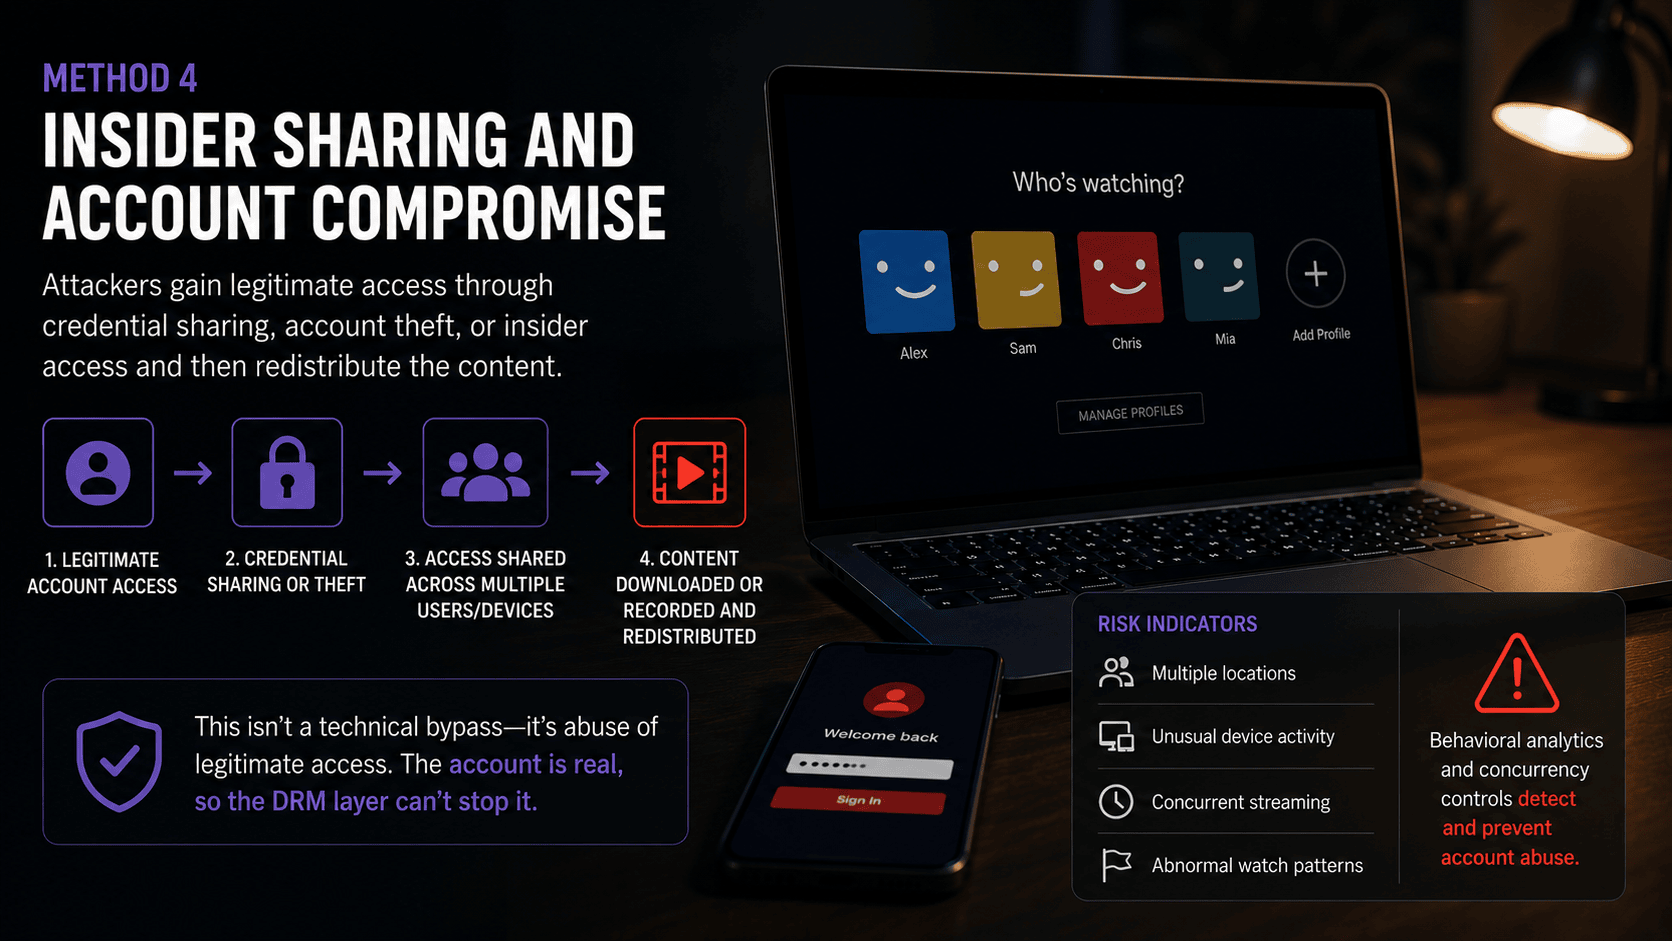
Three of the four bypass categories on this list require either sophisticated technical capability or specific hardware. This one requires neither.
For many content platforms, it accounts for a larger volume of real leaks than all three technical methods combined. And it is the category that exposes the most fundamental limitation of DRM as a single control: cryptography alone cannot solve a human access problem.
DRM is, at its core, a system that validates whether a license was properly issued to a session. It does not and cannot verify whether the person using that session is authorized to redistribute the content they are viewing.
The Categories of Insider Risk
Insider risk in a DRM context covers three overlapping scenarios.
The first is credential sharing: a user with a legitimate subscription shares their login, either with family members, colleagues, or more broadly through account-sharing schemes. The DRM system issues a valid license to each session because the credentials are valid. From the cryptographic perspective, everything is working correctly. The access policy is what has failed.
The second scenario is account compromise: credentials are stolen through phishing, credential stuffing, or data breach exposure. An attacker using compromised valid credentials receives a properly issued DRM license. The system has no cryptographic basis to distinguish this from a legitimate user.
The third scenario is insider sharing: an employee, partner, or vendor with legitimate access to content for business purposes (preview, quality review, localization) redistributes that content through non-cryptographic means. The license was entirely valid. The access was entirely authorized. The redistribution was not.
Platforms that invest in private video hosting with granular access controls reduce the blast radius of this attack category by limiting how many sessions can access high-value content simultaneously and by tying delivery tokens to specific session parameters that cannot easily be transferred.
How Behavioral Analytics and Concurrency Limits Detect This
The detection layer for insider risk operates above the cryptographic stack. It does not look at encryption or license validity. It looks at behavior.
Session-level behavioral analytics monitors playback patterns across an account and across a platform. The signals it tracks include simultaneous streams from geographically inconsistent locations, which is the most obvious indicator of shared credential use.
A single account streaming from two cities on different continents at the same time cannot represent one person.
Abnormal session frequency, device fingerprint mismatches, and access patterns that deviate significantly from an account’s historical baseline all feed the detection model.
Concurrency limits add a hard enforcement layer on top of the analytical one. By capping the number of simultaneous active streams per account and requiring re-authentication when that cap is reached, platforms create a rate-limiting control that makes large-scale credential sharing operationally impractical even if it cannot be cryptographically prevented.
Together, concurrency enforcement and behavioral session analytics form a detection layer that targets the human access surface DRM cannot address.
Is DRM Worth it, Even With These Gaps?
Having laid out four documented bypass categories, the next logical question is whether DRM is actually worth the implementation cost and operational complexity. It is the right question to ask. The honest answer, grounded in the actual evidence, is yes, unambiguously.
DRM’s gaps are real, narrow, and well-defined. They require technical skill levels, hardware access, or organizational proximity that the vast majority of would-be pirates do not have and are not motivated to acquire.
The target audience for casual piracy is not researchers, not security engineers, and not insiders with privileged access. It is subscribers who would prefer not to pay, which is precisely the category DRM was designed to address.
The Protection Math: What DRM Actually Stops
MUSO’s annual piracy intelligence reports track global piracy volumes across film, television, software, music, and publishing.
Their data consistently shows that the primary driver of casual piracy is accessibility: the content is unavailable in a viewer’s region, priced beyond what they consider reasonable, or simply inconvenient to access through legitimate channels.
DRM works because it transforms every one of those cases into a barrier that a non-technical user cannot bypass.
That is a different statement from “DRM is unbreakable.” It is a statement about who tries to pirate content and what stops them.
The overwhelming majority of piracy attempts are opportunistic, low-effort, and deterred by any meaningful technical barrier. Is DRM worth it for this population? The entire streaming industry, which has universally deployed it, has answered that question with billions of dollars of implementation investment.
Where DRM’s Real Value Lies
The platforms with the largest content libraries and the most aggressive anti-piracy budgets, Netflix, Disney+, Amazon, and Apple TV+, all use DRM as their primary protection layer.
That adoption is not a marketing decision. It is an engineering and economic one made by organizations with the resources to use any alternative they found superior.
None of them have abandoned DRM, because the foundational value it provides against casual piracy is irreplaceable by any single alternative control.
DRM is not enough on its own for the highest-risk content categories. That is not a criticism of DRM. It is a statement about what any single-layer security control can accomplish.
A deadbolt is not enough home security on its own either, but that does not make deadbolts useless. It makes the case for deadbolts plus an alarm plus a camera, each layer covering the gap the previous one leaves.
The Defense Stack That Actually Stops Leaks
Each of the four bypass categories covered in this article maps to a specific architectural weakness in DRM as a standalone control.
And each maps to a specific layer that fills that weakness. The pattern is consistent across all four: DRM does its part, a specific gap remains, a specific control closes it.
The teams that actually stop leaks are not the teams with the most expensive DRM license. They are the teams that identify where their content is most vulnerable and layer the right controls on top. Working with experienced penetration testing companies can help uncover security weaknesses, identify potential entry points, and strengthen protection before attackers exploit those gaps.
Dynamic Watermarking as the Forensic Tracing Layer
Forensic watermarking fills the gap left by screen recording on software DRM (Method 1) and by insider redistribution (Method 4).
It does not prevent the initial capture or sharing from happening. What it does is ensure that any redistributed copy carries a traceable session-level identifier that survives re-encoding, compression, and format conversion.
When a leaked copy is found in the wild, the watermark identifies the exact original session. That transforms an otherwise anonymous leak into an attributable event. Enforcement actions, including account suspension, legal notice, or takedown requests, become based on evidence rather than suspicion.
Gumlet’s dynamic watermarking operates at this forensic-grade level: embedding invisible, session-specific identifiers into every stream, not just visible overlays. The invisible marker survives re-encoding and is tied to the exact delivery token that issued the playback license.
Forensic watermarking and DRM protect at different points in the delivery chain. DRM prevents unauthorized playback before decryption. Forensic watermarking enables post-distribution attribution after decryption. The two are complementary, not redundant.
Behavioral Analytics as the Detection Layer
Behavioral analytics fills the gap left by account compromise and insider sharing (Method 4). It operates independently of the cryptographic stack, which means it catches exactly what DRM cannot: anomalous use of valid credentials.
Real-time session monitoring, concurrency enforcement, device fingerprinting, and geo-location analysis build a behavioral baseline for each account. Significant deviations from that baseline trigger investigation or automated enforcement.
An account that suddenly streams from three countries over 24 hours has not broken any encryption. The behavioral layer catches it anyway.
This layer is also the one most closely associated with the detection of organized credential sharing, where a single account’s credentials are distributed across many users. The concurrent session count is the first signal. Geolocation diversity and device fingerprint inconsistency confirm it.
What a Complete Layered Defense Looks Like
The three-layer model that follows from this analysis is not a theoretical construct. It is the architecture that the documented bypass categories make necessary:
Layer 1: DRM
DRM (Widevine, FairPlay, PlayReady) encrypts content and enforces license-based playback controls. It stops casual piracy at the access layer, which is the vast majority of unauthorized access attempts.
Layer 2: Forensic watermarking
Forensic watermarking embeds session-level identifiers in every stream. It enables post-distribution attribution, deters screen recording through the consequence of traceability rather than through prevention, and provides the evidentiary basis for enforcement.
Layer 3: Session-level behavioral analytics and concurrency controls
Session-level behavioral analytics and concurrency controls monitor playback behavior across sessions and accounts. They detect human-layer piracy, including insider sharing, credential abuse, and account compromise, that cryptography cannot address.
The citable takeaway from this framework: DRM + forensic watermarking + behavioral analytics is the complete piracy defense architecture. Each layer covers the gap the previous one leaves. No single layer is sufficient. Together, they create a stack where what bypasses one layer gets caught by the next.
Gumlet’s dynamic watermarking, specifically, operates as forensic watermarking: session-level identifiers embedded invisibly in every stream, surviving re-encoding and format conversion, and tied to the exact delivery token that issued the playback license.
Video platforms that offer all three capabilities as native, integrated features rather than requiring separate vendor integrations significantly reduce the implementation complexity this stack would otherwise demand.
Gumlet’s layered video protection features are built on exactly this architecture, combining DRM enforcement, forensic watermarking, and session analytics in a single platform.
Teams that treat DRM as the complete answer to content protection will, eventually, encounter one of the four gaps this article describes. Teams that layer it correctly will have the detection and attribution infrastructure in place before that day arrives.
Protect High-Value Content With Access Controls
Not every marketing asset needs DRM.
A public LinkedIn post obviously does not.
But stronger access controls can make sense for:
- paid courses;
- premium research;
- training libraries;
- paid webinars;
- members-only video;
- partner content;
- pre-release campaigns.
Before adding protection, ask:
What would actually be lost if this content were freely redistributed?
If the answer is:
“Nothing, because we want maximum reach”
then aggressive access control may work against the marketing objective.
If the content itself is the product, stronger controls make more sense.
Use Watermarking for Attribution
Watermarks do not need to prevent copying to be useful.
They can help identify where content came from.
There are several different types.
Visible Watermarks
These may contain:
- company logo;
- username;
- email;
- account ID;
- recipient information.
They can deter casual redistribution because ownership remains obvious.
Forensic Watermarks
These are designed to be less visible.
A session-specific identifier can potentially help connect a leaked asset to its distribution source.
This can be useful for:
- premium training;
- screeners;
- unreleased campaign videos;
- partner material;
- confidential presentations.
The objective shifts from:
prevent every copy
to:
make unauthorized redistribution attributable.
Use AI Watermarking for Generated Marketing Assets
AI content creates a new provenance challenge.
Was the image:
- photographed;
- generated;
- edited with AI;
- partially generated;
- copied from somewhere else?
Machine-readable watermarking helps provide additional context.
Google’s SynthID embeds invisible signals in AI-generated:
- images;
- video;
- audio;
- text.
Google now reports more than 180 billion watermarked images and videos.
For marketing teams, this has several implications.
It can help organizations:
- identify AI-created campaign material;
- improve internal asset governance;
- verify where certain media originated;
- create clearer AI disclosure workflows;
- reduce confusion between genuine and synthetic assets.
Google also applies SynthID and C2PA metadata to content generated inside its advertising tools.
AI provenance is becoming part of marketing operations.
Add Content Credentials to Your AI Content Workflow
Content Credentials are based on the C2PA standard.
They are designed to provide tamper-evident information about how digital media was created or modified.
The metadata can include information such as:
- creator or issuer;
- tool used;
- creation process;
- edits;
- AI involvement.
C2PA describes the technology as a way to provide verifiable provenance so people and systems can better understand a piece of media’s origin and history.
Adobe already applies Content Credentials automatically to assets fully generated with Adobe Firefly.
These credentials can identify Adobe as the issuer and show which generative AI tool was involved.
For marketers, Content Credentials can become a useful part of:
- asset management;
- creator attribution;
- approval workflows;
- AI disclosure;
- brand trust.
Protect Your Brand, Not Only the File
Copyright infringement is only one digital-content risk.
AI also makes brand impersonation easier.
A bad actor could potentially create:
- fake advertisements;
- cloned spokesperson content;
- fake endorsements;
- false product announcements;
- manipulated campaign images;
- fake customer-support videos.
The original asset may not even have been copied directly.
That means traditional copyright tools may not detect the problem.
Marketing and brand teams should also monitor:
- company name;
- executive names;
- product names;
- logos;
- campaign slogans;
- spokesperson likenesses;
- branded images.
The question is no longer only:
“Did someone copy our video?”
It can also be:
“Is someone using AI to make content that appears to come from us?”
Monitor YouTube Reuploads
For marketers creating original video, YouTube provides several copyright-management layers.
Its Copyright Match Tool automatically scans for full or nearly full copies of videos uploaded after the original.
Creators can then:
- archive a match;
- contact the uploader;
- request removal.
YouTube warns that a match does not automatically mean copyright infringement. Fair use, licensing, or another copyright exception may apply.
This distinction is important.
Detection is not the same as legal judgment.
Use automated systems to surface potential problems.
Use human review to decide what they mean.
Decide Whether to Remove, Monetize or Ignore Copies
Not every reuse deserves the same response.
A useful framework is:
| Situation | Possible Marketing Response |
|---|---|
| Unauthorized premium content | Consider removal |
| Fake branded advertisement | Report and investigate quickly |
| Influencer reused content with permission | Leave it live |
| Fan repost creating useful exposure | Evaluate before enforcing |
| Licensed partner use | No enforcement needed |
| Large platform reupload | Consider removal or monetization options |
| Short commentary clip | Review context and copyright exceptions |
YouTube’s own data shows why this decision matters.
Rights holders choose monetization on more than 90% of Content ID claims rather than blocking the content.
Sometimes reach has value.
Sometimes control matters more.
Make the decision strategically.
Protect AI Marketing Assets Before They Leave Your Team
Content protection should start during production.
Create an asset workflow that tracks:
- original creator;
- creation tool;
- AI model;
- source files;
- licenses;
- approved versions;
- publication locations;
- usage rights;
- expiration dates.
For important content, this makes later enforcement much easier.
Imagine finding your campaign video on another account six months after launch.
Can you immediately prove:
- when it was created;
- who created it;
- which assets were licensed;
- which version was published first?
If that information lives across six Slack messages and someone’s Downloads folder, enforcement becomes considerably harder.
Treat provenance as part of content operations.
AI Content Protection Can Improve Brand Trust
Protection is not only defensive.
Provenance can also help establish authenticity.
As synthetic media becomes more convincing, companies may increasingly benefit from demonstrating:
This really came from us.
That can matter for:
- executive communications;
- product announcements;
- branded videos;
- advertising;
- press assets;
- creator collaborations.
C2PA’s Content Credentials are specifically designed to preserve information about how an asset was created and changed.
This creates an interesting marketing shift.
Digital provenance is not only:
“How do we catch theft?”
It can also become:
“How do customers verify authenticity?”
AI Training Preferences Are Becoming Part of Content Rights
AI introduces another rights-management question:
Can our content be used by AI systems?
Adobe Content Authenticity allows creators to attach a generative-AI training and usage preference through Content Credentials.
The preference can indicate that the creator does not want supported AI systems to train on or use the content for certain generative features.
Adobe generative AI training preference guidance
Support is not universal.
But the direction is important.
Content rights management increasingly includes:
Who can view it?
Who can copy it?
Who can modify it?
and now:
Who can use it in AI workflows?
Marketing teams should expect these questions to become more common.
Measure Content Leakage Like a Marketing Metric
Content protection should not operate in a reporting vacuum.
Track metrics such as:
| Metric | What It Shows |
|---|---|
| Unauthorized Copies Found | Scale of redistribution |
| Platforms Affected | Where copying happens |
| Views on Copies | Potential audience impact |
| Revenue Lost or Recovered | Commercial effect |
| Copies Monetized | Revenue recovered from reuse |
| Takedown Success Rate | Effectiveness of enforcement |
| Time to Detection | How quickly misuse is found |
| Time to Resolution | How quickly the issue is handled |
| False Matches | Quality of the monitoring process |
One viral unauthorized upload may matter more than 100 copies nobody watches.
Prioritize according to business impact.
The AI Marketing Content Protection Decision Framework
Not every asset deserves maximum protection.
Use this simple framework.
High Value + Restricted
Examples:
- paid courses;
- premium research;
- unreleased campaigns.
Use stronger access controls, watermarking, monitoring, and enforcement.
High Value + Public
Examples:
brand films;
original research;
flagship videos.
Prioritize provenance, fingerprinting, monitoring, and attribution.
Low Value + Public
Examples:
- normal social media posts;
- promotional graphics.
Aggressive protection may create more work than value.
Focus mainly on brand impersonation or commercially harmful reuse.
High Virality Potential
Examples:
- original short-form video;
- memes;
- creator campaigns.
Monitoring becomes particularly important because redistribution can spread rapidly.
The question should always be:
What are we protecting, and what would unauthorized use actually cost us?
Closing Thoughts
DRM is not a vault. It was never designed to be one. It is a first layer, and a highly effective one for the specific category of piracy it was built to stop: casual, opportunistic, low-skill unauthorized access. That category represents the vast majority of the more than 215 billion annual visits to piracy sites that MUSO tracks across the global content ecosystem.
The four documented bypass methods are real. Screen recording on software DRM, HDCP downgrade attacks, Widevine L3 key extraction, and insider sharing each represent a specific architectural gap.
Each also represents a known, addressable problem. Forensic watermarking closes the recording gap. Hardware L1 enforcement closes the key extraction gap. Behavioral analytics closes the insider gap.
The platforms that actually stop leaks are not the ones with the most sophisticated DRM configuration in isolation. They are the ones that have layered DRM, forensic watermarking, and behavioral analytics into a coherent stack, understanding that what slips past one layer will be caught by the next.
Treat DRM as the first line of defense, not the only one. The complete architecture is the combination. And for platforms distributing content where a single leak could mean lost revenue, broken licensing agreements, or eroded audience trust, that combination is not optional. It is the baseline.
Frequently Asked Questions About DRM Security
1. Can DRM be completely defeated?
DRM cannot be defeated through a single universal bypass, but four documented attack categories exist that can circumvent it under specific conditions.
Each category requires technical expertise, specialized hardware, or insider access that the majority of pirates do not have. For the vast majority of piracy attempts, including all casual and opportunistic access, DRM is an effective and proven deterrent.
2. What is the difference between Widevine L1 and Widevine L3?
Widevine L1 processes content decryption inside a Trusted Execution Environment (TEE), a hardware-isolated chipset that never exposes the content key to software memory. Widevine L3 performs decryption in software within the browser or application process, which creates a potential key exposure surface.
Major platforms require Widevine L1 for HD and HDR content delivery because of the documented key extraction risk associated with L3.
3. Does DRM prevent screen recording?
DRM does not fully prevent screen recording on software-only (L3) implementations. L3 DRM decrypts video frames in memory before they reach the display, and a sufficiently equipped attacker can capture those frames at the render stage.
L1 hardware DRM, combined with forensic watermarking, addresses this by restricting high-quality output to hardware-enforced paths and enabling post-capture attribution through session-level identifiers embedded in every stream.
4. What is forensic watermarking, and how is it different from DRM?
DRM prevents unauthorized access to content before it is decrypted. Forensic watermarking embeds an invisible, session-specific identifier into each video stream after decryption, which survives re-encoding and redistribution.
The two controls protect at different points in the delivery chain: DRM blocks unauthorized playback, and forensic watermarking enables attribution if content is redistributed after legitimate playback.
5. Is DRM worth the cost and complexity for video platforms?
For any platform distributing premium or paid content, yes. DRM stops casual piracy, which represents the overwhelming volume of unauthorized access attempts, and is used universally by Netflix, Disney+, and Amazon not because it is perfect but because it demonstrably works.
The four documented bypass categories affect a narrow, technically sophisticated subset of attackers. The answer to those gaps is layered controls, not abandoning DRM.
6. What is the best way to stop video piracy completely?
No single technology stops piracy completely. The most effective approach is a layered defense: DRM as the access control layer, forensic watermarking as the post-distribution tracing layer, and behavioral analytics as the human-layer detection system.
Together, these three layers address all four documented bypass categories and create a content protection architecture where casual piracy is blocked, sophisticated capture is traceable, and insider abuse is detectable.
Other Interesting Articles
- AI LinkedIn Post Generator
- Gardening YouTube Video Idea Examples
- AI Agents for Gardening Companies
- Top AI Art Styles
- Pest Control YouTube Video Idea Examples
- Automotive Social Media Content Ideas
- Plumber YouTube Video Idea Examples
- AI Agents for Pest Control Companies
- Electrician YouTube Video Idea Examples
- How Pest Control Companies Can Get More Leads
- AI Google Ads for Home Services
- 60-Second Training Videos Are the New Corporate Standard
- Cybersecurity PR Pricing: Retainers, Deliverables & ROI
- Best AI Tools for Product Consistency in E-Commerce Video
Master the Art of Video Marketing
AI-Powered Tools to Ideate, Optimize, and Amplify!
- Spark Creativity: Unleash the most effective video ideas, scripts, and engaging hooks with our AI Generators.
- Optimize Instantly: Elevate your YouTube presence by optimizing video Titles, Descriptions, and Tags in seconds.
- Amplify Your Reach: Effortlessly craft social media, email, and ad copy to maximize your video’s impact.